


 For all latest news, follow the Daily Sun's Google News channel.
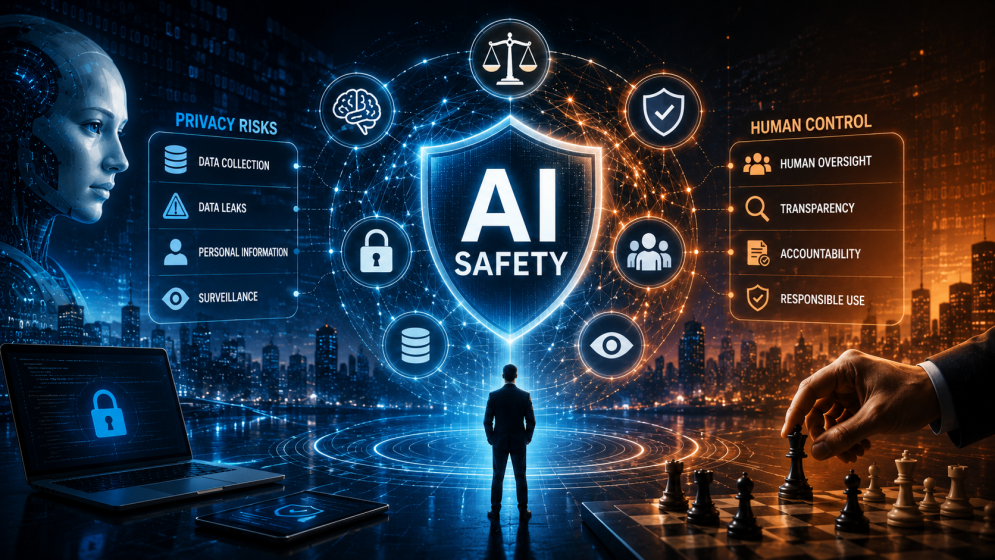
An illustration representing AI safety, data privacy and human oversight in artificial intelligence.
Artificial Intelligence (AI) is becoming an integral part of our daily lives. From chatbots and search engines to sectors like healthcare, education, and financial services, AI systems assist humans in making decisions, processing information, and completing various tasks. However, as these technologies become increasingly capable, questions regarding their safety, reliability, and impact on humans continue to grow.
AI systems can process vast amounts of data, generate credible content, and complete various tasks with minimal human intervention. At the same time, however, they can also provide incorrect information, leak sensitive data, amplify existing biases, or exhibit behaviors that neither their creators nor their users could have anticipated.
This raises an important question: How can artificial
intelligence be created or used responsibly while protecting people, their data
and their interests? This is where the issue of 'AI safety' comes to the fore.What
Is AI Safety?
AI safety refers to the research, design, development and
use of artificial intelligence systems in ways that reduce the risk of harm to
people and society. It involves making AI systems reliable, secure, transparent
and consistent with human values and expectations.
AI safety is not limited to preventing technical errors. It
also includes protecting personal information, reducing harmful bias, limiting
the spread of misinformation and ensuring that humans can oversee important
decisions made with AI assistance.
For example, an AI-powered healthcare system should not
provide misleading medical recommendations without appropriate safeguards.
Similarly, an AI tool used in financial services should handle customer
information responsibly and allow qualified people to review important
decisions.
In simple terms, AI safety aims to ensure that artificial
intelligence works as intended, does not create unnecessary harm and remains
subject to meaningful human oversight.
AI Privacy Risks: How Does AI Affect Personal Data?
Privacy is one of the major concerns surrounding the growing
use of artificial intelligence. Many AI systems rely on data to learn patterns,
generate responses and provide personalised services. Depending on how a system
is designed and operated, this data may include personal details, user
interactions, images, voice recordings, location information or other sensitive
information.
If such information is collected, stored or processed
without appropriate safeguards, it can create privacy risks.
Collection and Use of Personal Information
People may share personal or sensitive information when
using AI chatbots, virtual assistants and other digital services. They might
enter work documents, financial details, private messages or information about
their personal lives.
Users do not always know how a particular service handles
the information they provide. Depending on the provider's policies and
settings, data may be stored, reviewed or used to improve services. This makes
it important to understand the privacy policy and data controls of an AI
platform before sharing sensitive information.
Data Leaks and Unauthorised Access
AI services can become targets for cyberattacks, just like
other digital platforms. If an organisation fails to protect its systems and
databases, personal or confidential information could be exposed through a data
breach.
The consequences may include identity theft, financial
fraud, reputational damage or the disclosure of confidential business
information.
AI and Facial Recognition
Some AI technologies can identify or analyse people using
facial images, voice patterns and other biometric information. These tools have
applications in identity verification and security systems, but their use also
raises questions about consent, surveillance and the protection of biometric
data.
The responsible use of such technologies requires clear
rules about what information can be collected, why it is needed, who can access
it and how long it should be retained.
Major Risks Associated With AI Systems
Privacy is only one part of the wider AI safety challenge.
AI systems can create other risks depending on their capabilities, training
data, design and the way people use them.
Bias and Discrimination
AI systems learn patterns from data. If the information used
to train them contains historical bias or does not adequately represent
different groups of people, the systems may produce unfair results.
For example, an AI-based recruitment tool could disadvantage
certain applicants if its training data reflects biased hiring patterns.
Similarly, automated decision-making systems may produce unequal outcomes in
areas such as lending, education or public services.
Reducing these risks requires representative data, careful
testing, regular evaluation and human review of consequential decisions.
Misinformation and AI-Generated Content
Generative AI tools can create text, images, audio and
videos that appear realistic. While these capabilities support creativity,
communication and productivity, they can also be misused to produce misleading
information.
AI-generated deepfakes, fabricated images and synthetic
audio can make it difficult for people to distinguish authentic material from
manipulated content. Such content may be used for scams, impersonation,
harassment or the spread of false claims.
AI systems can also generate inaccurate information in
response to ordinary questions. These errors are sometimes described as AI
hallucinations. Users should therefore verify important information,
particularly when it relates to health, law, finance or public safety.
Unpredictable or Unreliable Outputs
AI systems do not always produce consistent or correct
results. A model may provide a useful answer in one situation but generate an
inaccurate or inappropriate response in another.
This becomes particularly concerning when AI is used in
sensitive environments. Organisations should test systems under different
conditions, monitor their performance and establish procedures for correcting
errors.
The Challenge of Human Control
As AI systems become more advanced, maintaining meaningful
human control is an important part of AI safety.
Some AI tools can now perform multi-step tasks, analyse
information and make recommendations with limited supervision. In certain
settings, automated systems may also influence decisions that affect people's
employment, finances, education or access to services.
The challenge is to ensure that people remain able to
understand, supervise and intervene in these processes.
Human Oversight in Important Decisions
AI can support decision-making, but it should not
automatically replace human judgement in every situation. Decisions involving
people's rights, safety or well-being may require qualified human review.
For example, an AI system may help a doctor analyse medical
information, but medical professionals should remain responsible for
interpreting the results and deciding on appropriate treatment.
Transparency and Accountability
People should be able to understand when AI is being used in
important processes and what role it plays in producing a result. Organisations
developing or deploying AI systems should also establish clear responsibility
for monitoring their performance and addressing harmful outcomes.
Without transparency and accountability, it can become
difficult to identify why an AI system made a particular decision or who is
responsible when something goes wrong.
Preventing Excessive Dependence on AI
AI tools can make everyday tasks easier, but relying on them
without verification can create problems. Users may accept incorrect answers,
overlook important context or allow automated recommendations to influence
decisions without sufficient consideration.
Human judgement, critical thinking and independent
verification therefore remain essential when working with AI.
How Can AI Systems Be Made Safer?
Creating safer AI systems requires cooperation among
developers, technology companies, governments, organisations and users. No
single technical solution can address every risk. A combination of responsible
design, security measures, testing and human oversight is necessary.
Some important approaches include:
1. Protecting Personal Data: AI developers and
service providers should collect only the information they need, explain how it
is used and apply appropriate safeguards to prevent unauthorised access.
2. Testing AI Systems Regularly: Systems should be
evaluated before deployment and monitored afterwards to identify errors,
weaknesses, bias and unexpected behaviour.
3. Improving Transparency: Organisations should
provide clear information about an AI system's capabilities, limitations and
appropriate uses. Users should know when AI-generated content or automated
decisions are involved.
4. Maintaining Human Oversight: People should be able
to review important AI-assisted decisions, challenge incorrect outcomes and
intervene when a system behaves unexpectedly.
5. Reducing Bias: Developers should evaluate training
data and system outputs to identify unfair patterns. Testing should consider
different groups and real-world conditions.
6. Strengthening Security: AI systems should be
protected through access controls, secure data handling, regular updates and
appropriate cybersecurity practices.
7. Promoting Responsible AI Use: Users should avoid
sharing unnecessary sensitive information, verify important AI-generated claims
and understand the limitations of the tools they use.
The Future of AI Safety
AI technology is evolving rapidly, and safety challenges are
likely to become more complex as systems gain new capabilities and are
integrated into more areas of daily life.
Future AI safety efforts will need to address emerging
concerns, including increasingly realistic synthetic media, automated cyber
threats, privacy protection, biased decision-making and the behaviour of more
autonomous AI systems.
Governments and international organisations are also
developing frameworks and guidelines to encourage responsible AI development. The National Institute of Standards and Technology (NIST), for example, has
introduced the AI Risk Management Framework to help organisations identify and
manage risks throughout the AI lifecycle. UNESCO has also established a globalrecommendation on the ethics of artificial intelligence.
However, guidelines alone cannot guarantee safe outcomes.
Effective AI safety will depend on how these principles are translated into
real-world development practices, organisational policies and everyday use.
As AI becomes more deeply integrated into society,
maintaining a balance between technological progress, human oversight and
responsible innovation will remain a central challenge.
Conclusion: Building AI That Humans Can Trust
Artificial intelligence offers significant opportunities,
but its benefits depend on how responsibly it is developed and used. Privacy
risks, security weaknesses, bias, misinformation and the challenge of
maintaining human control all require careful attention.
AI safety is therefore an ongoing responsibility rather than
a one-time technical achievement. Developers must build reliable systems,
organisations must establish accountability, governments must create
appropriate safeguards and users must remain informed and cautious.
Ultimately, the goal is not to stop AI
innovation but to ensure that technological progress continues in a way that
protects people, respects their rights and keeps human interests at the centre.